
2025
University of Jordan
BSc in Cybersecurity
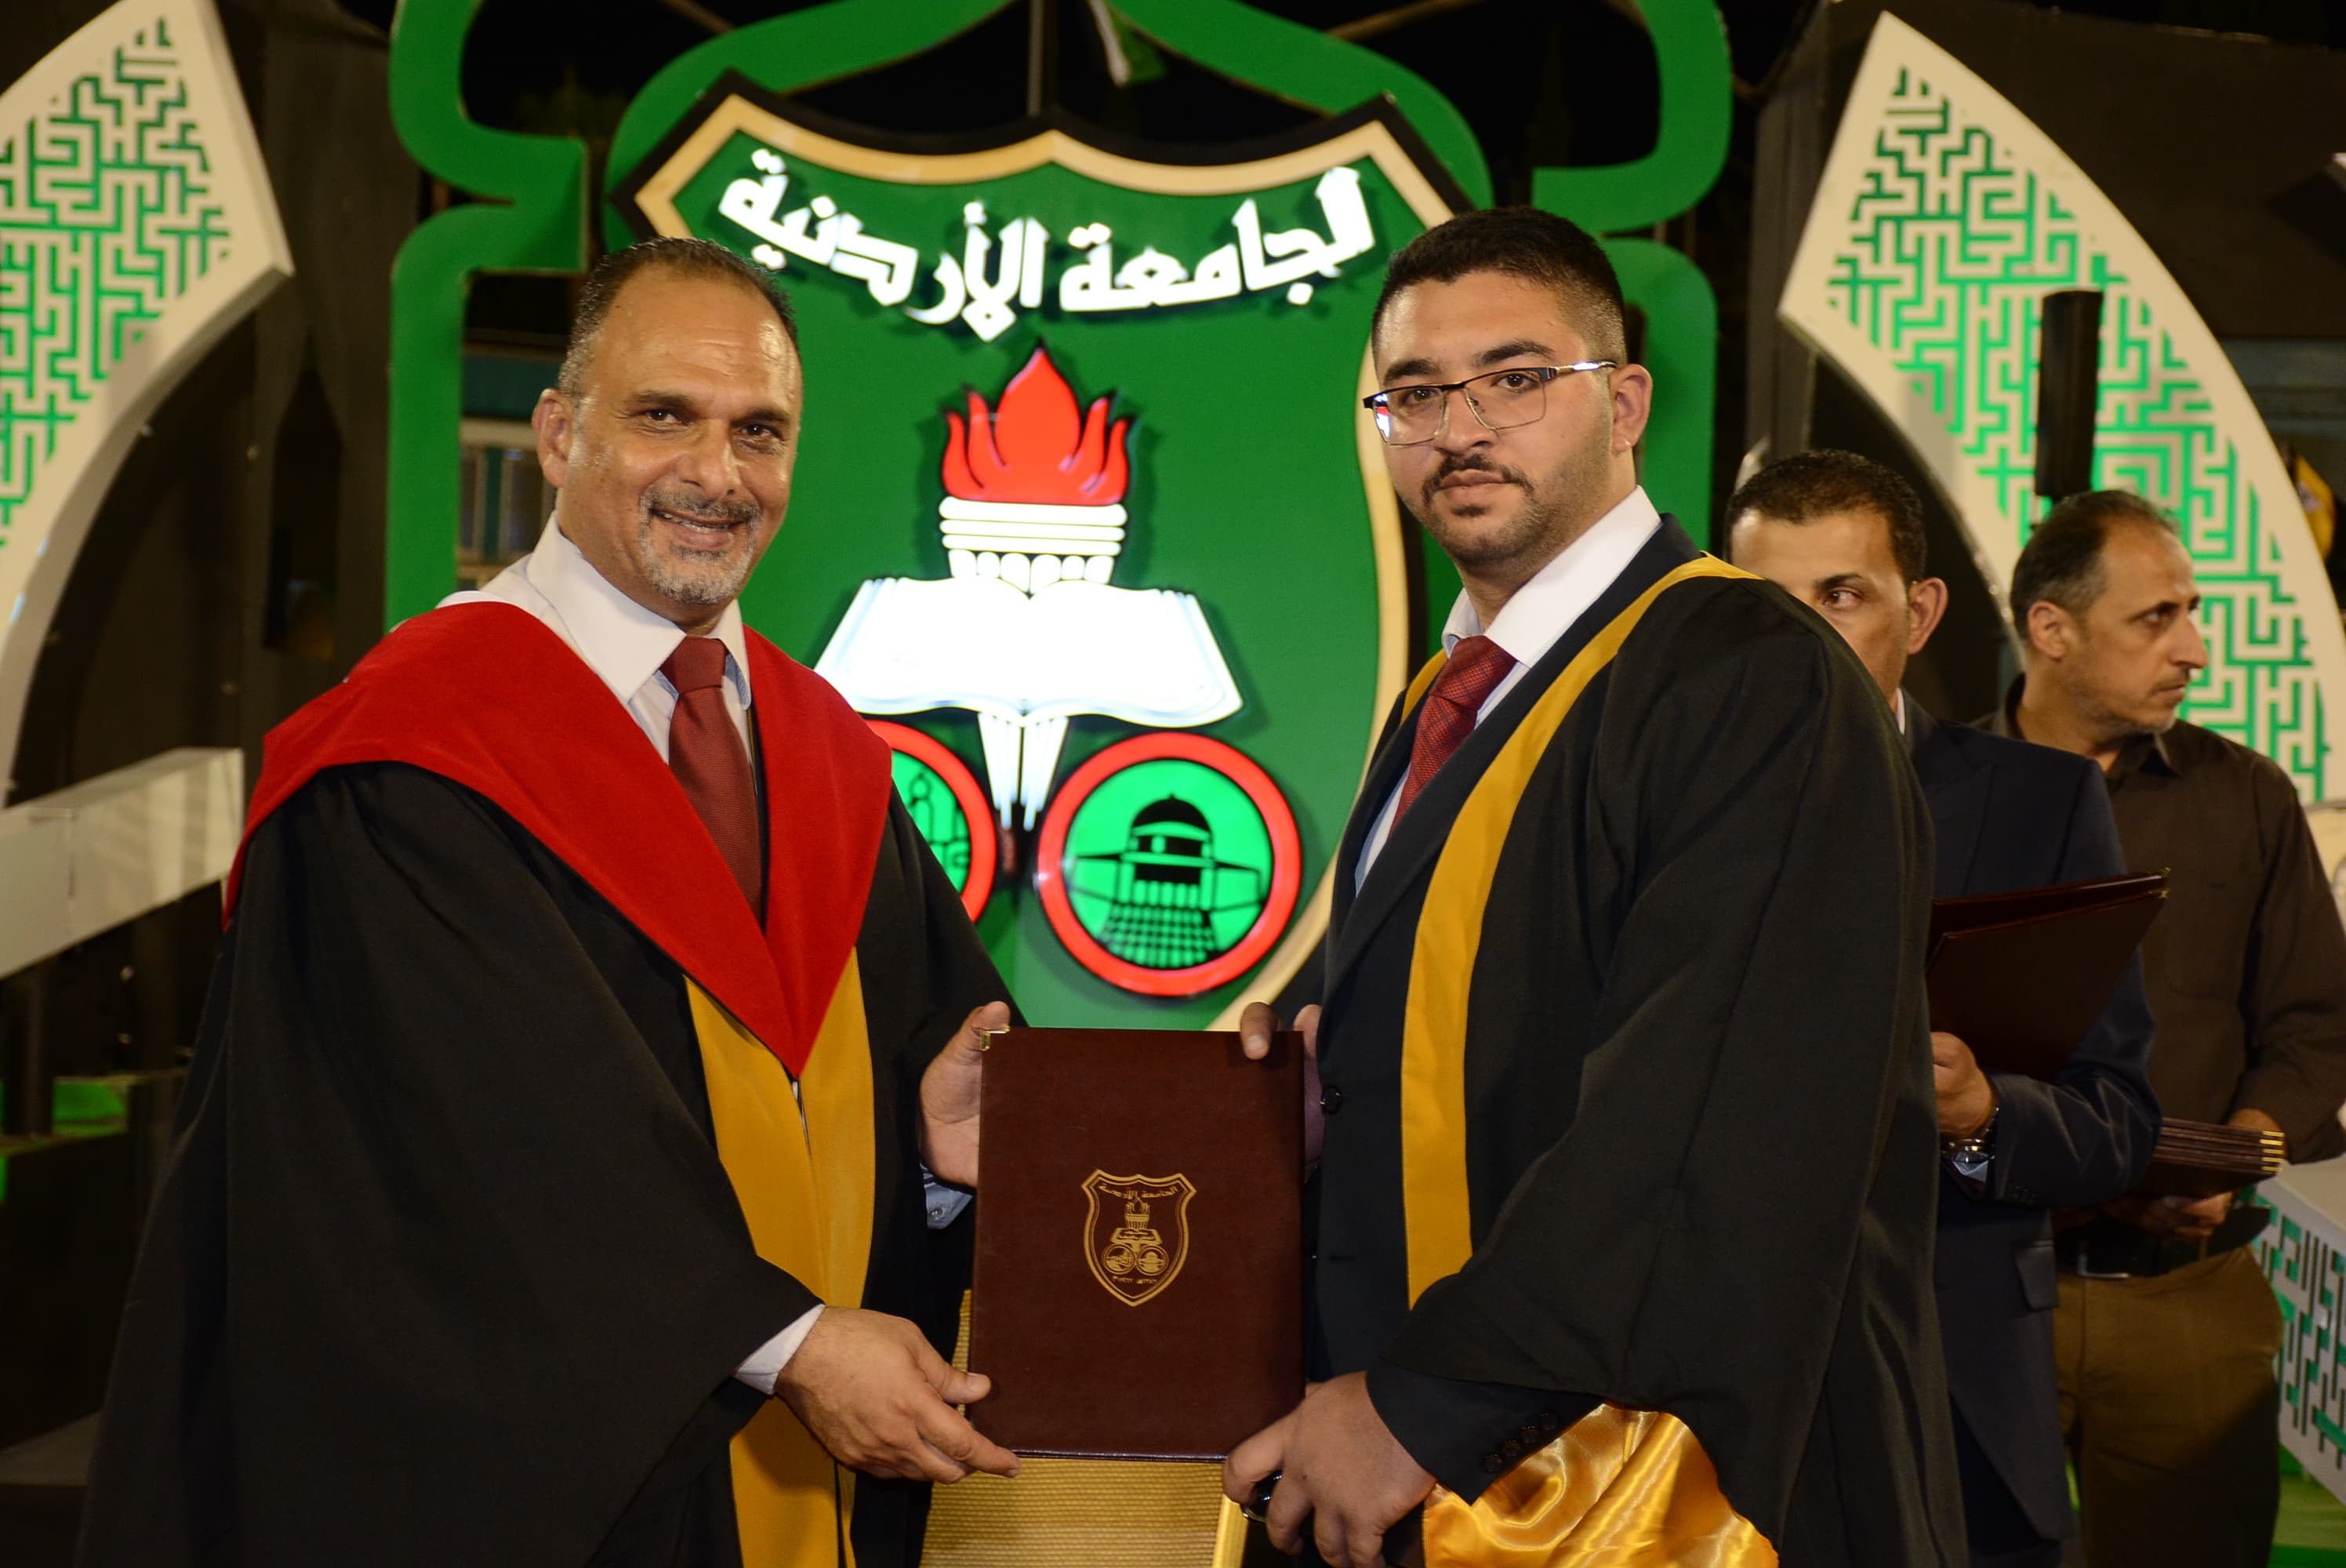
BSc graduation
Receiving the Bachelor of Science degree in Cybersecurity at the University of Jordan.
Personal archiveProfessional work spans offensive and defensive security, enterprise infrastructure, security operations, applied cybersecurity research, and software engineering.
Timeline
Project demonstrations, media coverage, and academic milestones organized by year.
2025
University of Jordan
BSc in Cybersecurity
Receiving the Bachelor of Science degree in Cybersecurity at the University of Jordan.
Personal archive2024
SOFEX Jordan / Aqaba
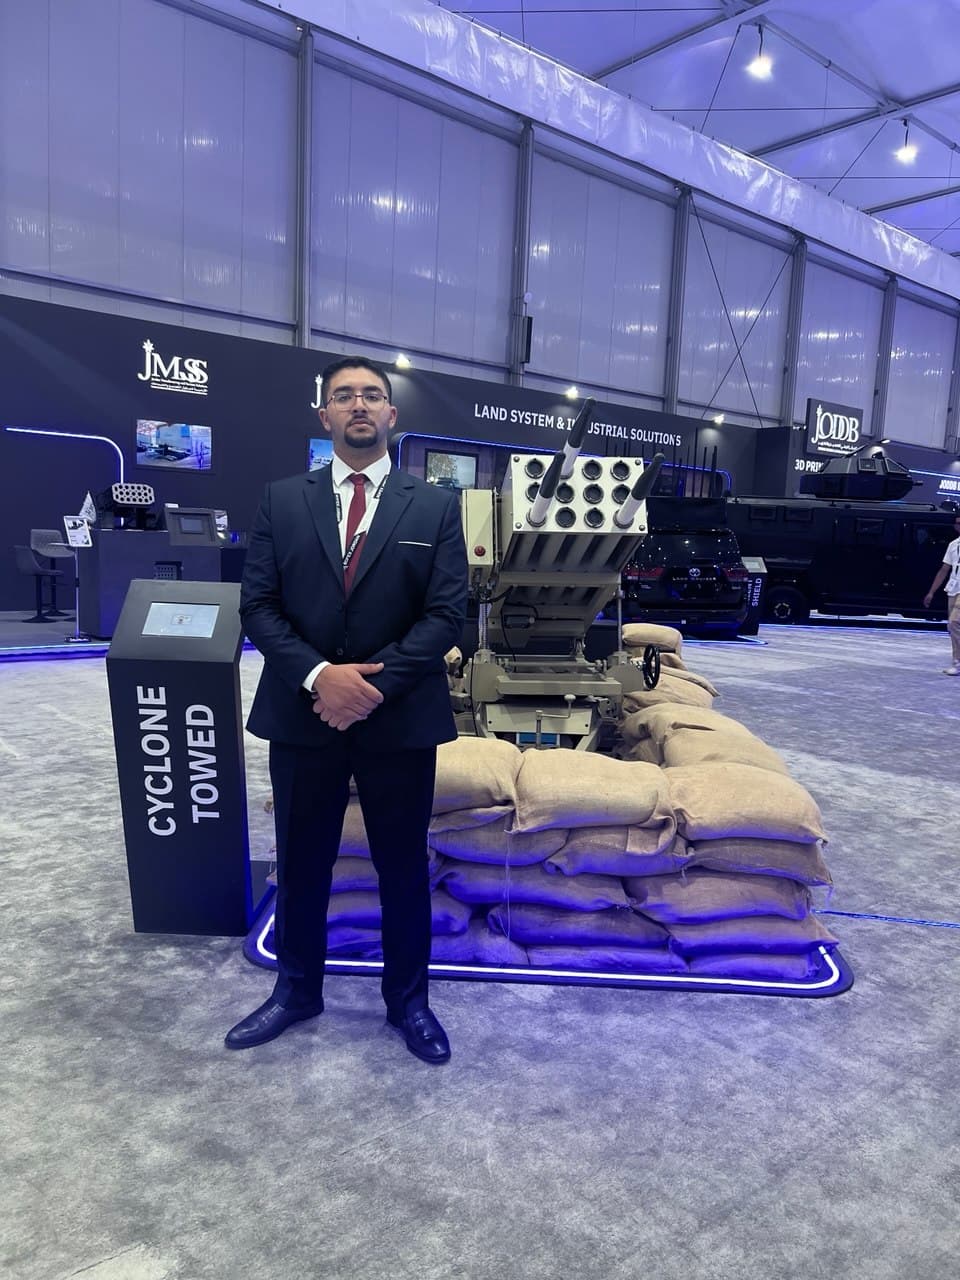
S2VC exhibition and royal visit
At the SOFEX exhibition in Aqaba, Jordan.
Personal archive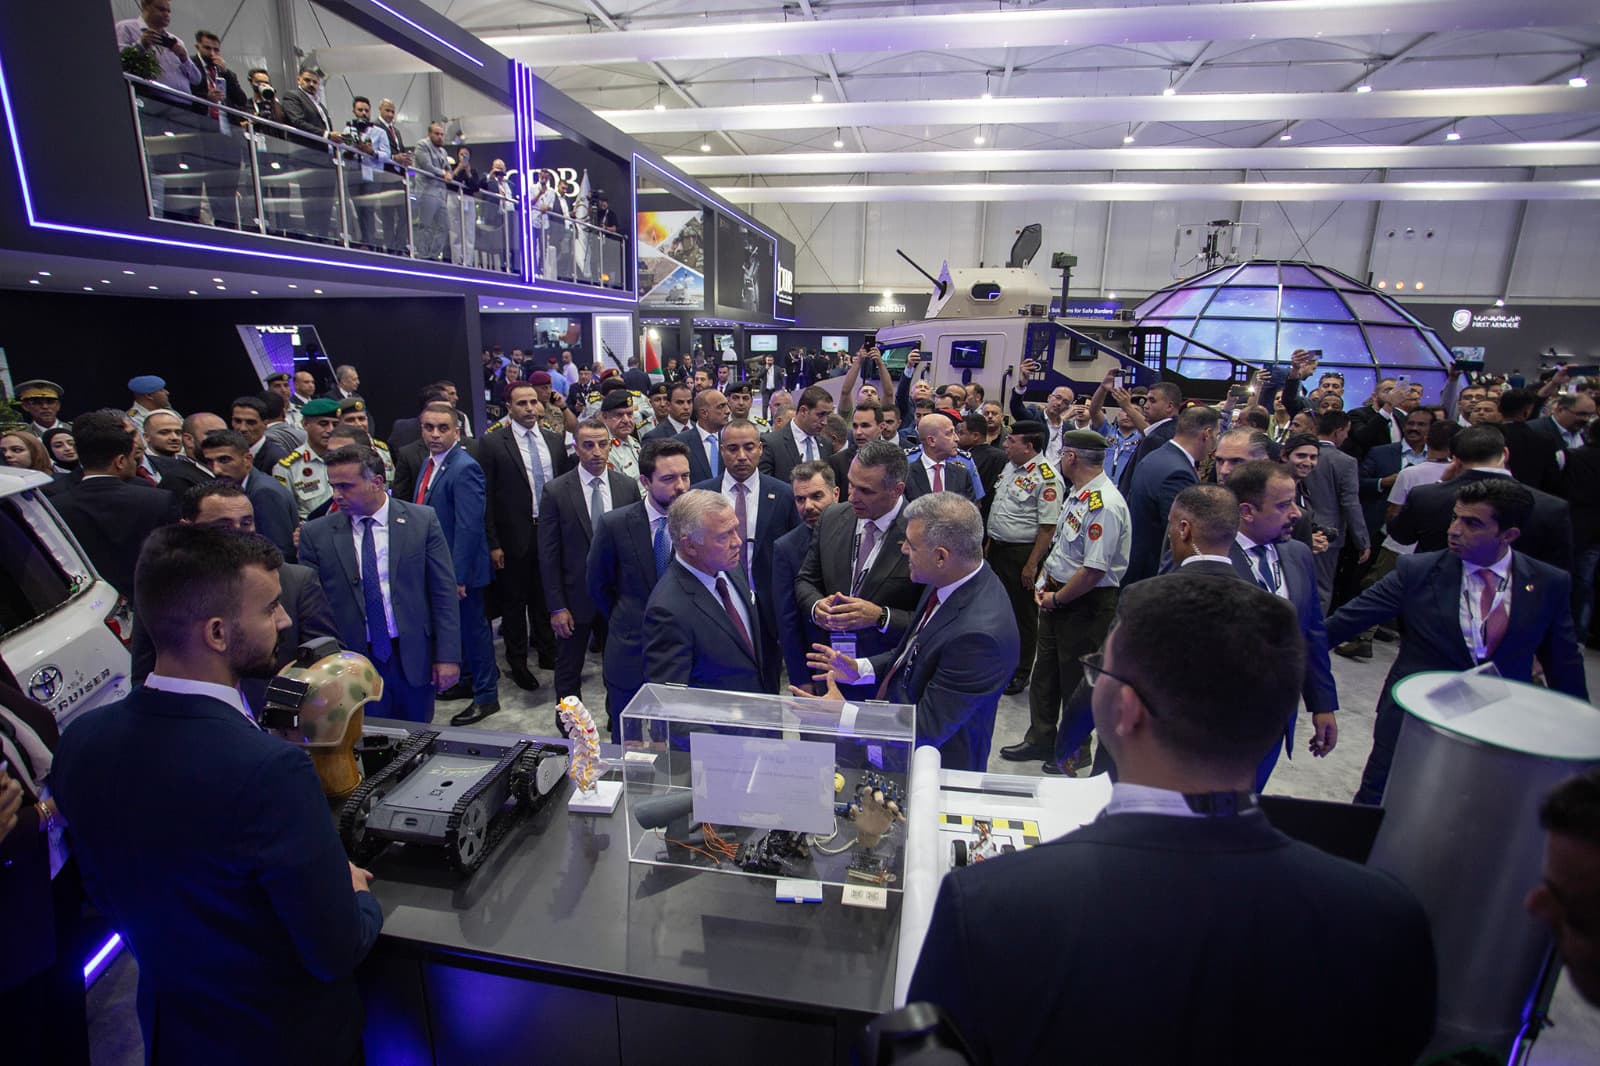
King Abdullah II visits the S2VC project display during SOFEX 2024 in Aqaba.
SOFEX 2024 archive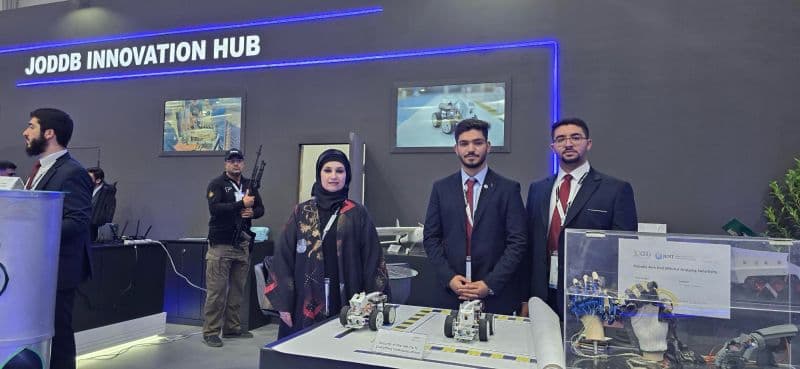
At the S2VC display inside the JODDB Innovation Hub during SOFEX 2024.
LinkedIn post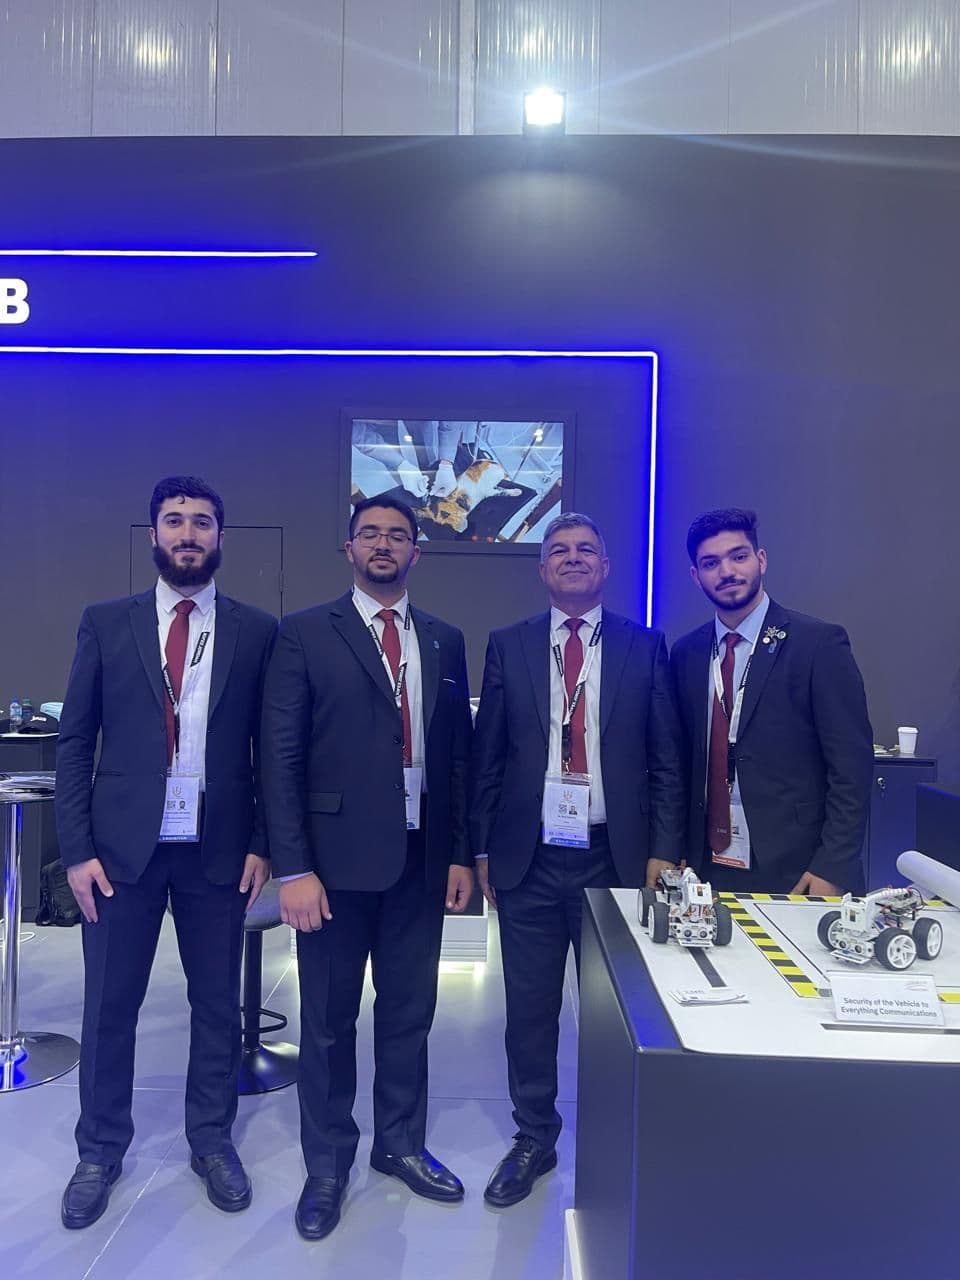
S2VC collaborators beside the physical project testbed in the JODDB Innovation Hub.
LinkedIn postServices
Test authentication, authorization, input handling, exposed services, privilege paths, and configuration weaknesses.
Deliverables
Education
BSc
University of Jordan
Amman, Jordan
Experience
Zayed University, UAE
May 2026 to present
Credentials
Each certification includes the issued document and its TCM Security verification page.

PNPT
TCM Security / Earned March 2, 2025

PSAA
TCM Security / Earned May 20, 2026
Research paper
IEEE / IJCC 2024 / pp. 70 to 75
The paper examines secure vehicle-to-everything communication through attack and defense scenarios, robot-car and virtual-road testbeds, a lightweight protocol, datasets, and machine-learning detection.
Iman Almomani, Wissam Almahasneh, Abdalhameed Aldradkeh, Suleiman Alfar, Mousa Al-Akhras, and Musa Alyaman
Projects
Production platform
A bilingual calculator platform for finance, education, cybersecurity, networking, health, business, and everyday use.
Open toolspilo.comEvent website
The official public website for TEDxBAU event information, agenda, speakers, sponsors, and visitor guidance.
Open tedxbau.orgResearch system
Research on secure smart vehicular communications, including V2X attack scenarios, physical and virtual testbeds, and machine-learning detection.
View paper on IEEECompetition environment
A cybersecurity competition designed around a multi-stage penetration-testing progression.
Graduation project
A vehicle-to-infrastructure simulation used to compare secure and adversarial communication scenarios.
Technical guides
Contact
Include the relevant system details, technical constraints, required outcome, and timeline. Security testing requires authorization from the system owner.